Founder-Led. Senior Certified Team.
Both founders are personally involved in every engagement. No juniors, no handoffs. Penetration testing, SOC 2 / ISO 27001 evidence, and platform programme submissions for startups in Bengaluru that don't have a dedicated security team.
You Work Directly With Us
You work with the people who run the engagement, not junior staff. Every engagement is led personally by our founders, backed by a certified team.
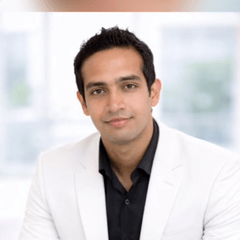
20+ years across IT infrastructure, networking, and platform engineering; security focus since founding Cybersecify in 2023. Ashok leads scoping, compliance readiness, and client delivery. He scopes every assessment, manages client delivery, and ensures every report meets investor and auditor expectations.
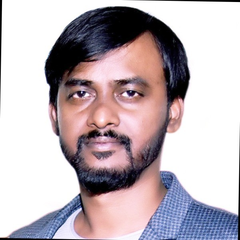
17+ years in IT and security, including 11 years in offensive security at MobileIron, Ivanti, and Amnic. Rathnakara leads all penetration testing engagements, vulnerability research, and security architecture reviews. His OSCP credential number is OS-101-34173.
Verify this OSCP on CredlyLike how we work? We take on exceptional people when the fit is right. See our jobs page.
We Maintain OpenEASD
OpenEASD is the open-source external attack surface discovery tool Cybersecify built and maintains, with or without community help. MIT-licensed, self-hostable via Docker, or run as a free hosted scan.
Both founders are hands-on in every engagement
6 Business Days Per Scope, Not Months
One scope is 6 business days from kick-off to report, and two is 12. For larger estates we confirm the schedule when we scope it. Engineer-friendly findings with fix guidance, not 200-page compliance documents.
Founder-Led & Reviewed
Every engagement is led and reviewed by both founders. OSCP, CISSP, CEH, CREST, CompTIA PenTest+ and ISO 27001 Lead Auditor across the team. The people who scope your engagement are the people who run it, and no junior analyst runs your pentest.
6 Clients/Month Cap
We limit active engagements so every client gets senior-only delivery. No rotating analysts, no learning on your time.
The Price Is Published, and It Is the Same for Everyone
You see the number before you ever talk to us. What sets it is the work you need: how many scopes, and what each one takes to test. See the published prices.
Nothing Is Invoiced Until Both Sides Sign
A mutual NDA covers what we discuss and anything either side shares. The SOW then fixes what we test, how long it takes and what you receive, signed by an authorised signatory on both sides. Only then does an invoice exist.
You Can Count Your Own Scopes First
Every scope boundary is published, so you can work out what you need and what it costs before you talk to us. We do not charge for a second scope unless the work genuinely demands one.
A Full Sample Report, No Email Gate
Thirty-three pages of a real report structure, ungated. Read the finding format, the evidence, the compliance mapping and the retest section before you decide anything. Read the sample report.
Offensive Security, One Team
Penetration testing and SOC 2 / ISO 27001 audit evidence your auditor can use. One founder-led team from first scope to retest.
Some of the Brands We've Worked With
Penetration testing across AI-first SaaS, HealthTech, e-commerce, and EdTech.


